An inventory is a process, not a spreadsheet. Any subdomain without a known owner eventually becomes nobody's asset.
Most attack surface inventory efforts start with a spreadsheet that stops matching reality a few months later. The problem is not the spreadsheet but how assets are born.
How an asset becomes unowned
- A subdomain created for a campaign is never decommissioned.
- A team spins up a test environment in its own cloud account, outside the corporate inventory.
- Domains from an acquisition are inherited but never recorded.
What looking from outside changes
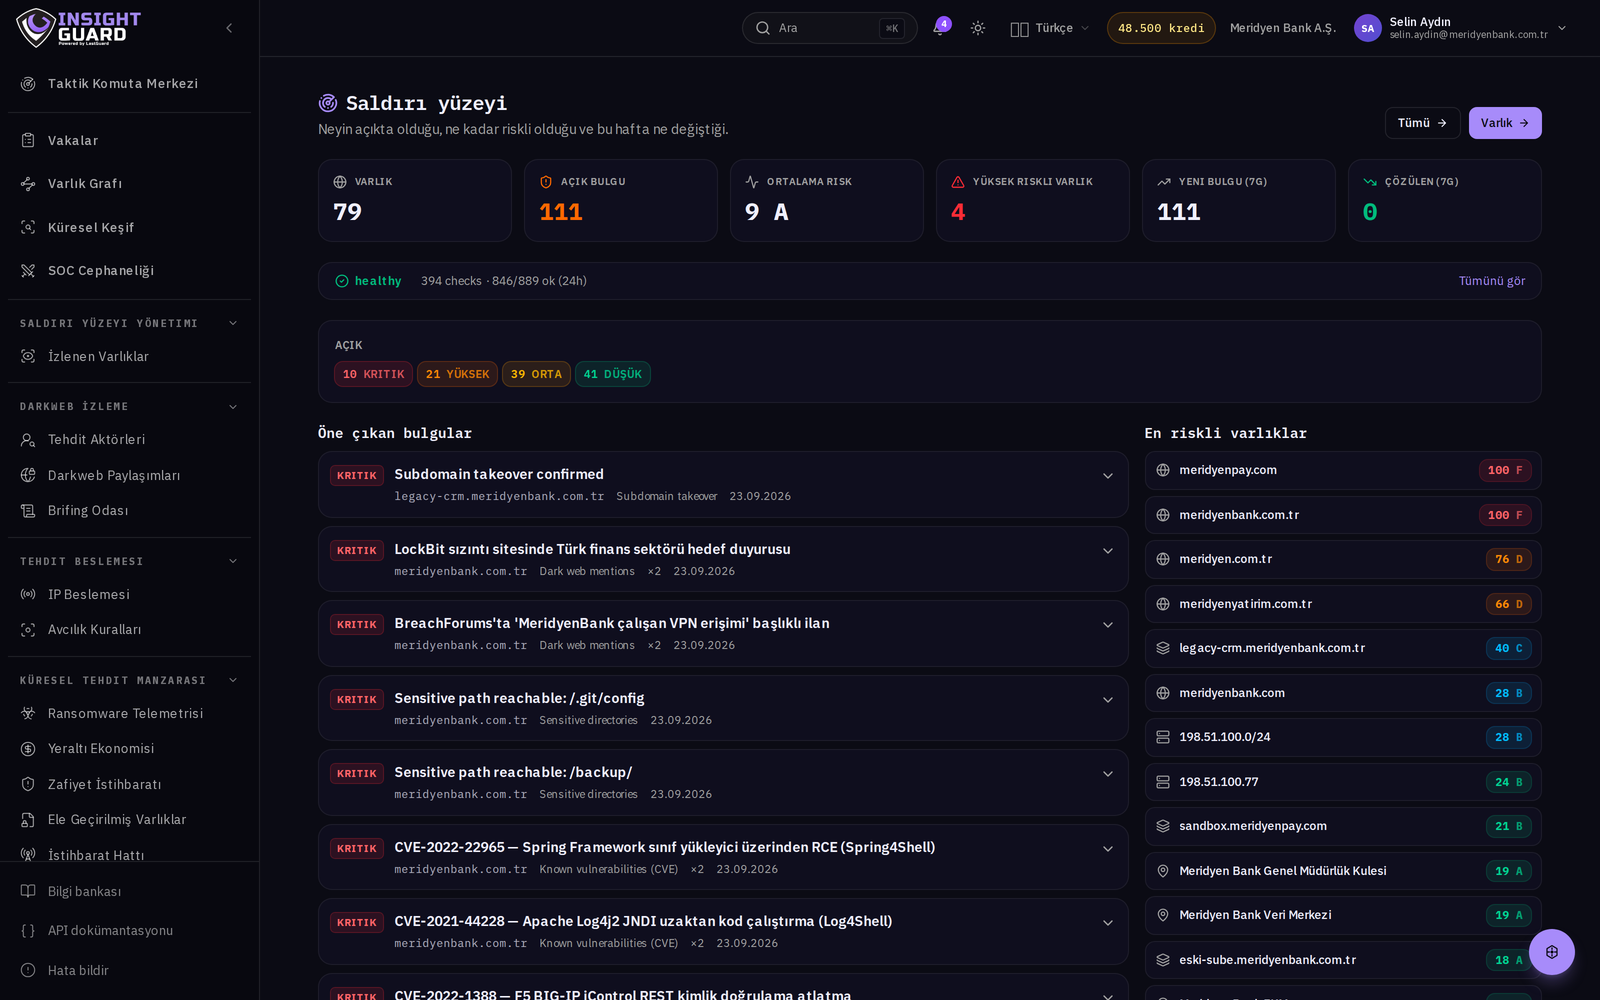
The internal inventory tells you what you built. An external scan tells you what the internet can see. The gap between them is where the attacker works.
Certificate transparency logs are the cheapest way to close that gap: every new name issued a certificate under your domain is recorded whether you asked or not.
A practical rule
Give every subdomain an owner and an expiry date. No record without an owner; every expiring record goes to review automatically.