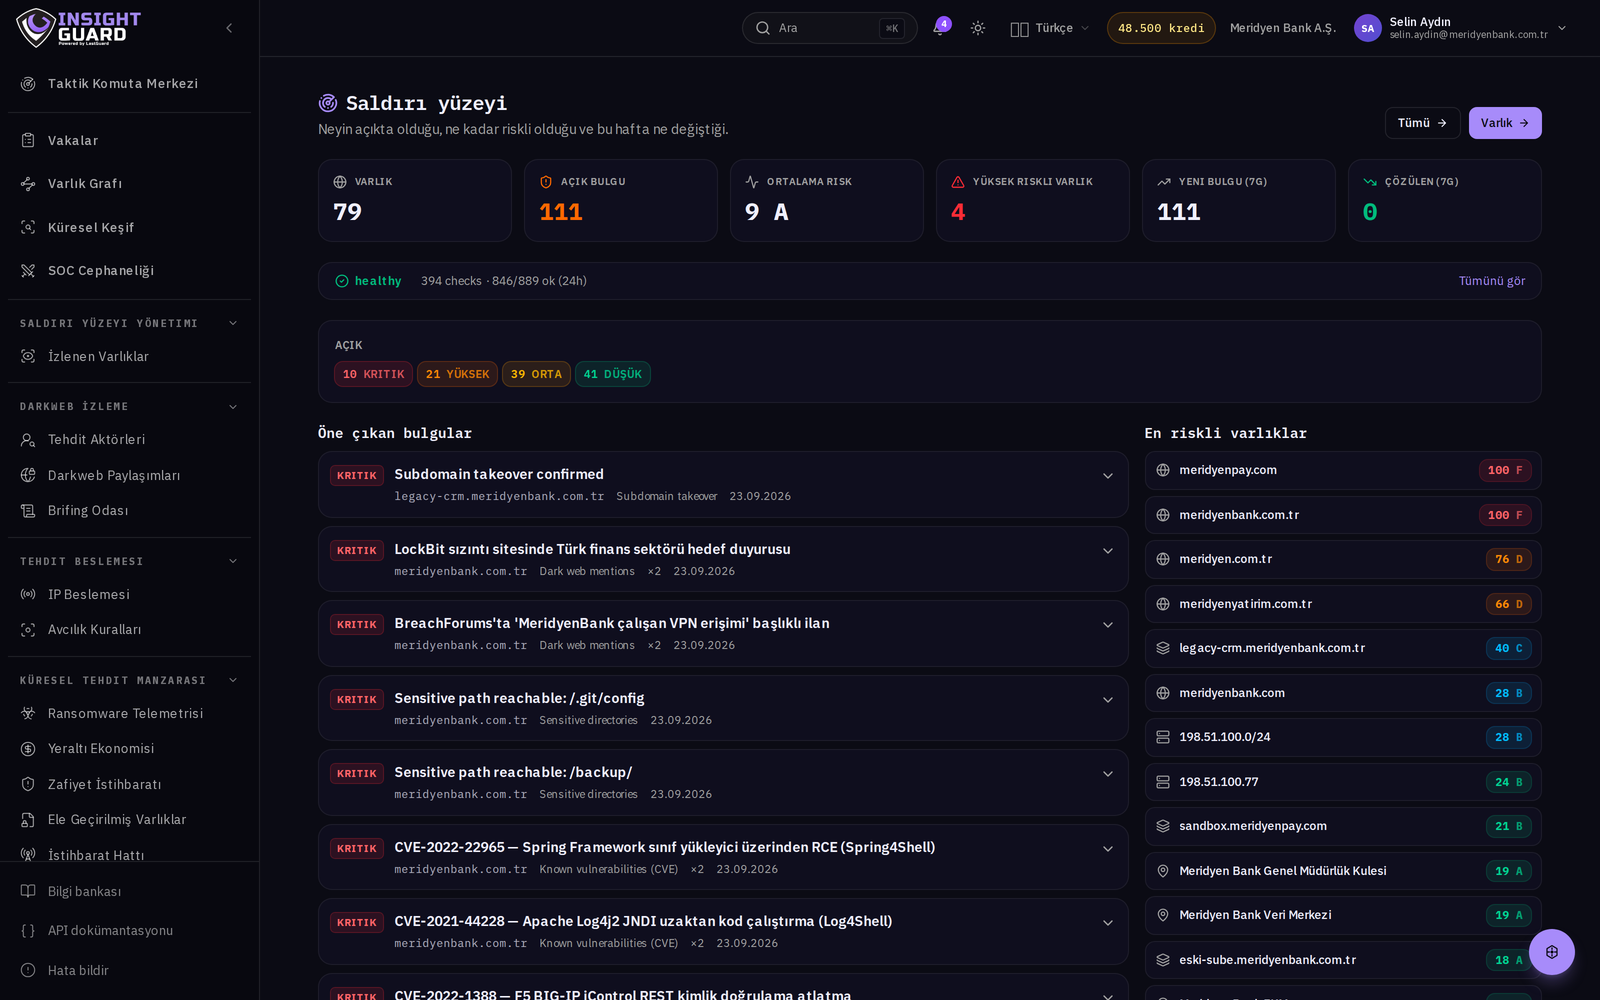
An annual supplier questionnaire starts ageing the moment the contract is signed. The externally visible surface can be measured continuously.
Most third-party risk programmes run on a question list. Even when answered in good faith, the answers are a snapshot and go unverified.
What can be measured externally
- The supplier's internet-facing admin panels and out-of-date services.
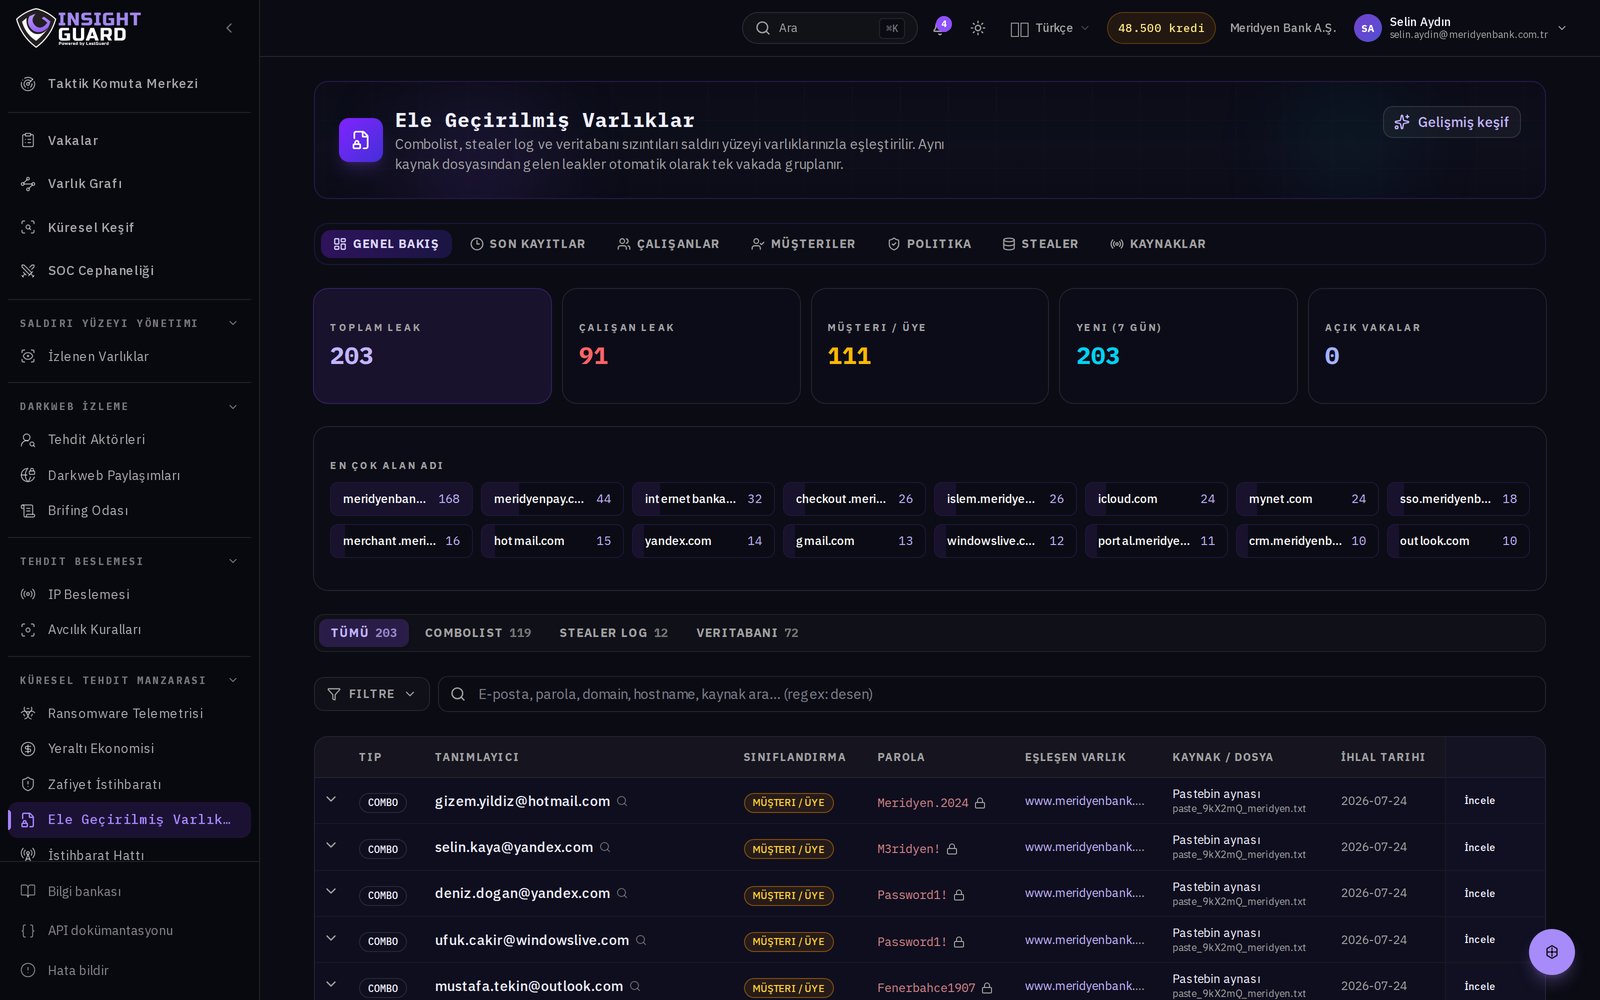
- Leaked credentials belonging to their staff, and whether those match corporate services.
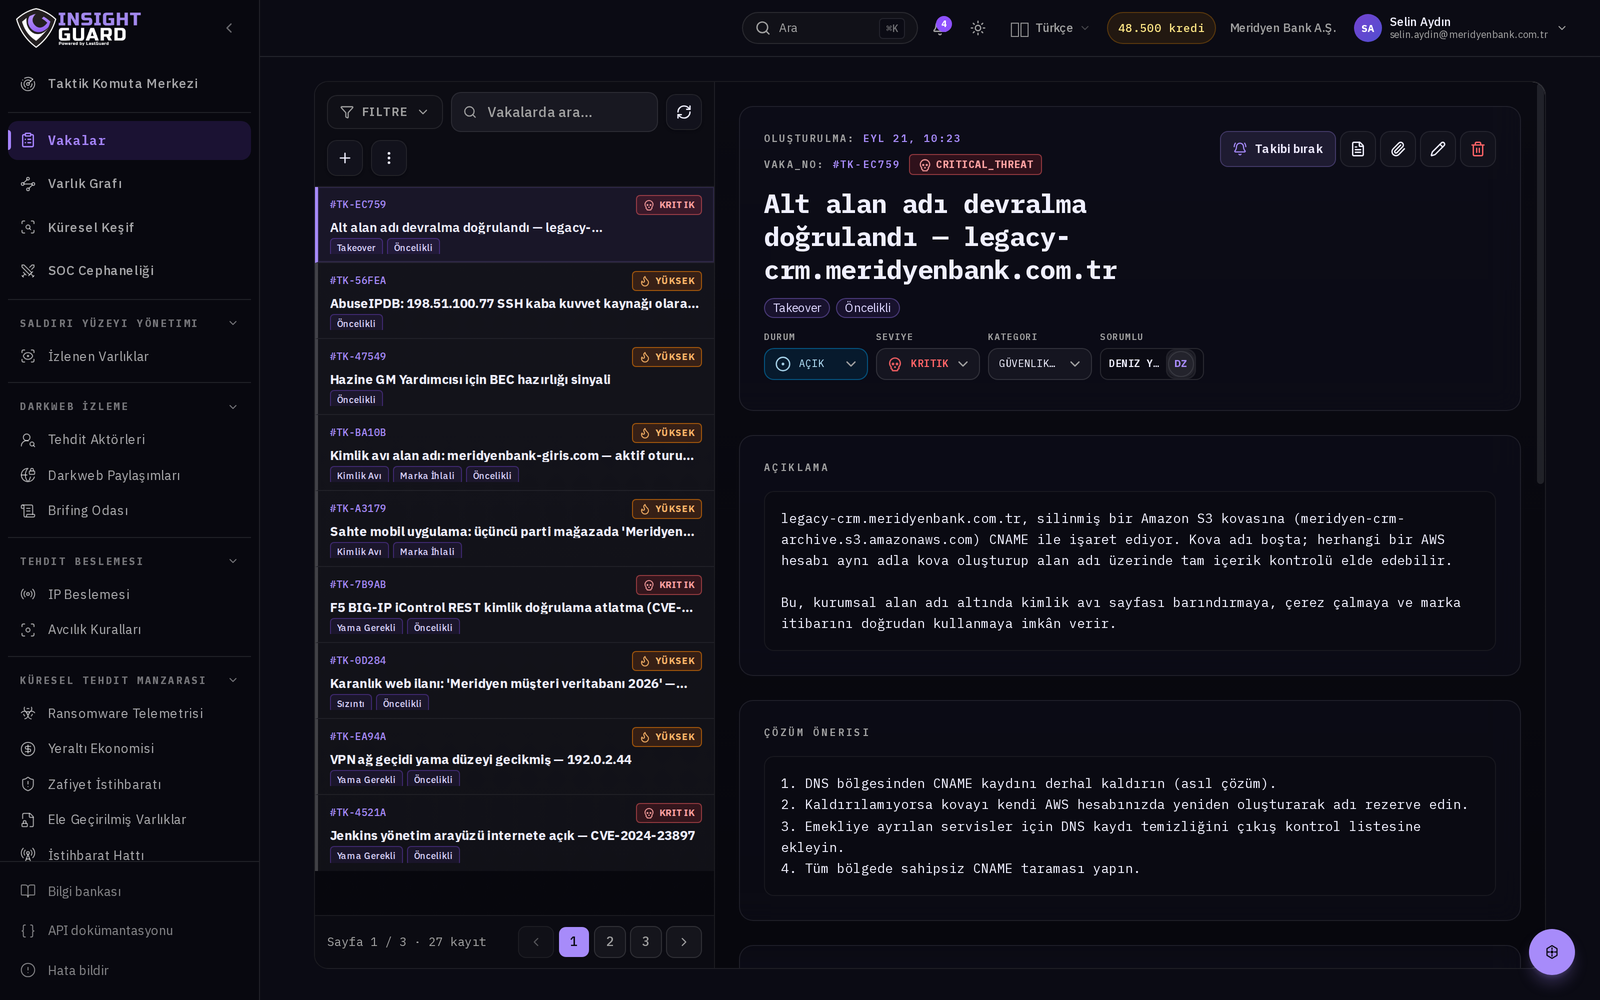
- Hygiene in certificate and DNS records: expired certificates, dangling subdomains.
- Mentions on leak sites and forums.
Tying it to the contract
Measurement alone changes nothing. Three clauses make it useful: incident notification time, response time for externally detected findings, and an obligation to declare subcontractors.
A scoping warning
Scanning a supplier's entire infrastructure is both unnecessary and legally awkward. Limit scope to assets that concern you: the domains serving you, the systems processing your data and the accounts reaching them.