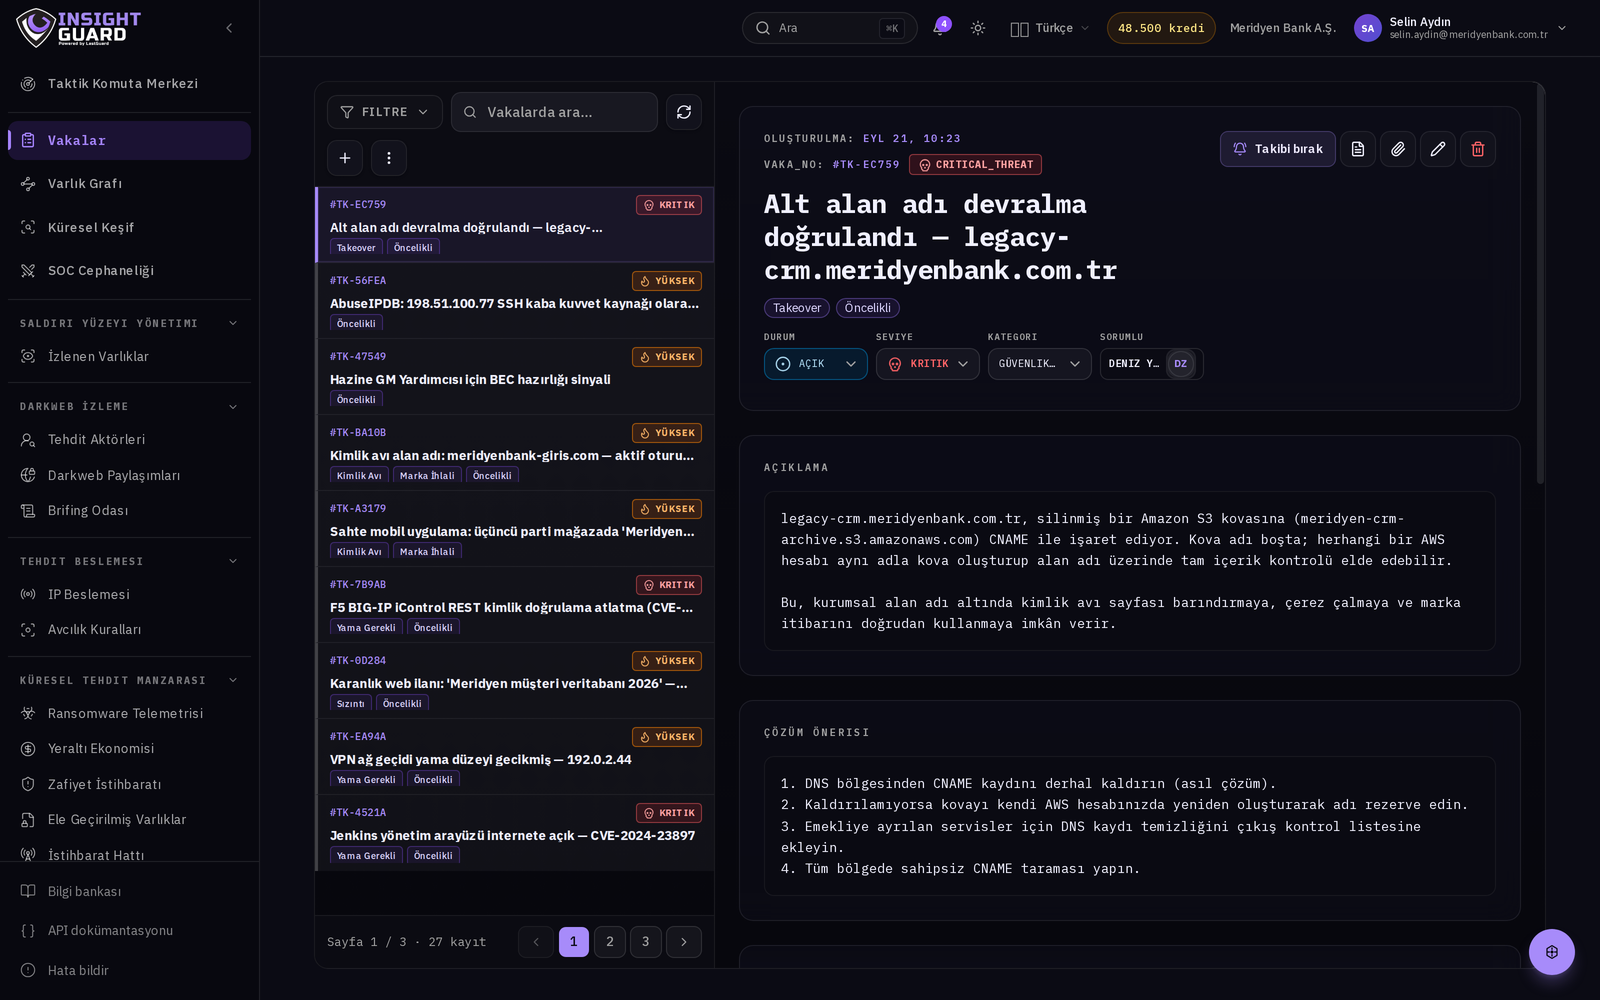
When a DNS record outlives the resource behind it, someone else can claim the name. Nobody notices, because nothing breaks.
If a subdomain points to a cloud resource and that resource is deleted, the DNS record remains. Whoever claims the same name next can publish content under your domain.
Why it goes unnoticed
Because the record was never deleted, no monitoring alarm fires. The page was already unused, so nobody visits it and the breakage is invisible.
Consequences
- A phishing page under your own domain — no browser warning, and users trust it.
- Session theft where cookie scope was written to the parent domain.
- Mail sent in your name if the record is tied to SPF/DKIM configuration.
The cleanup rule
A resource deletion is not complete until the DNS record is deleted. Bind that to a process rule; catching it with a control is cheaper than scanning for it afterwards.