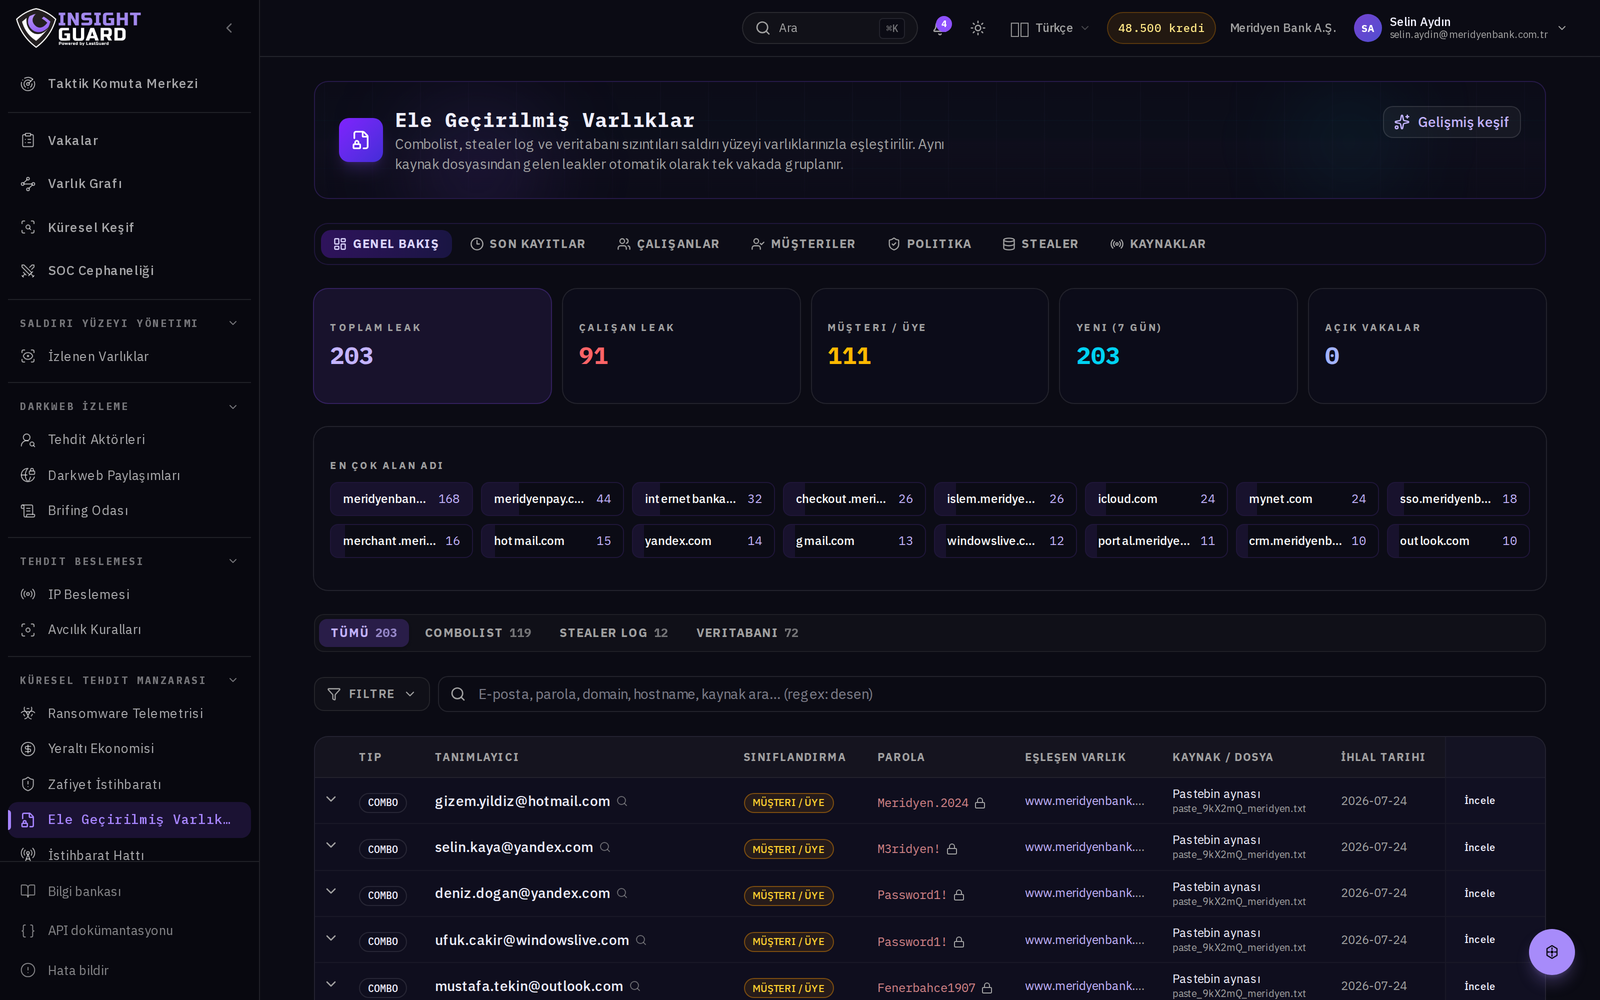
How to read a stealer log: the anatomy of one line
What sits inside an infostealer record, what each field tells you and in what order to triage it.

Blog
Short answers to questions we meet in the field: reading stealer logs, catching typosquats, managing IOCs, closing cases. Research, operations and product notes.
What sits inside an infostealer record, what each field tells you and in what order to triage it.
An indicator list does not gain value as it grows. Context-free IOCs create work for analysts and become a closed …
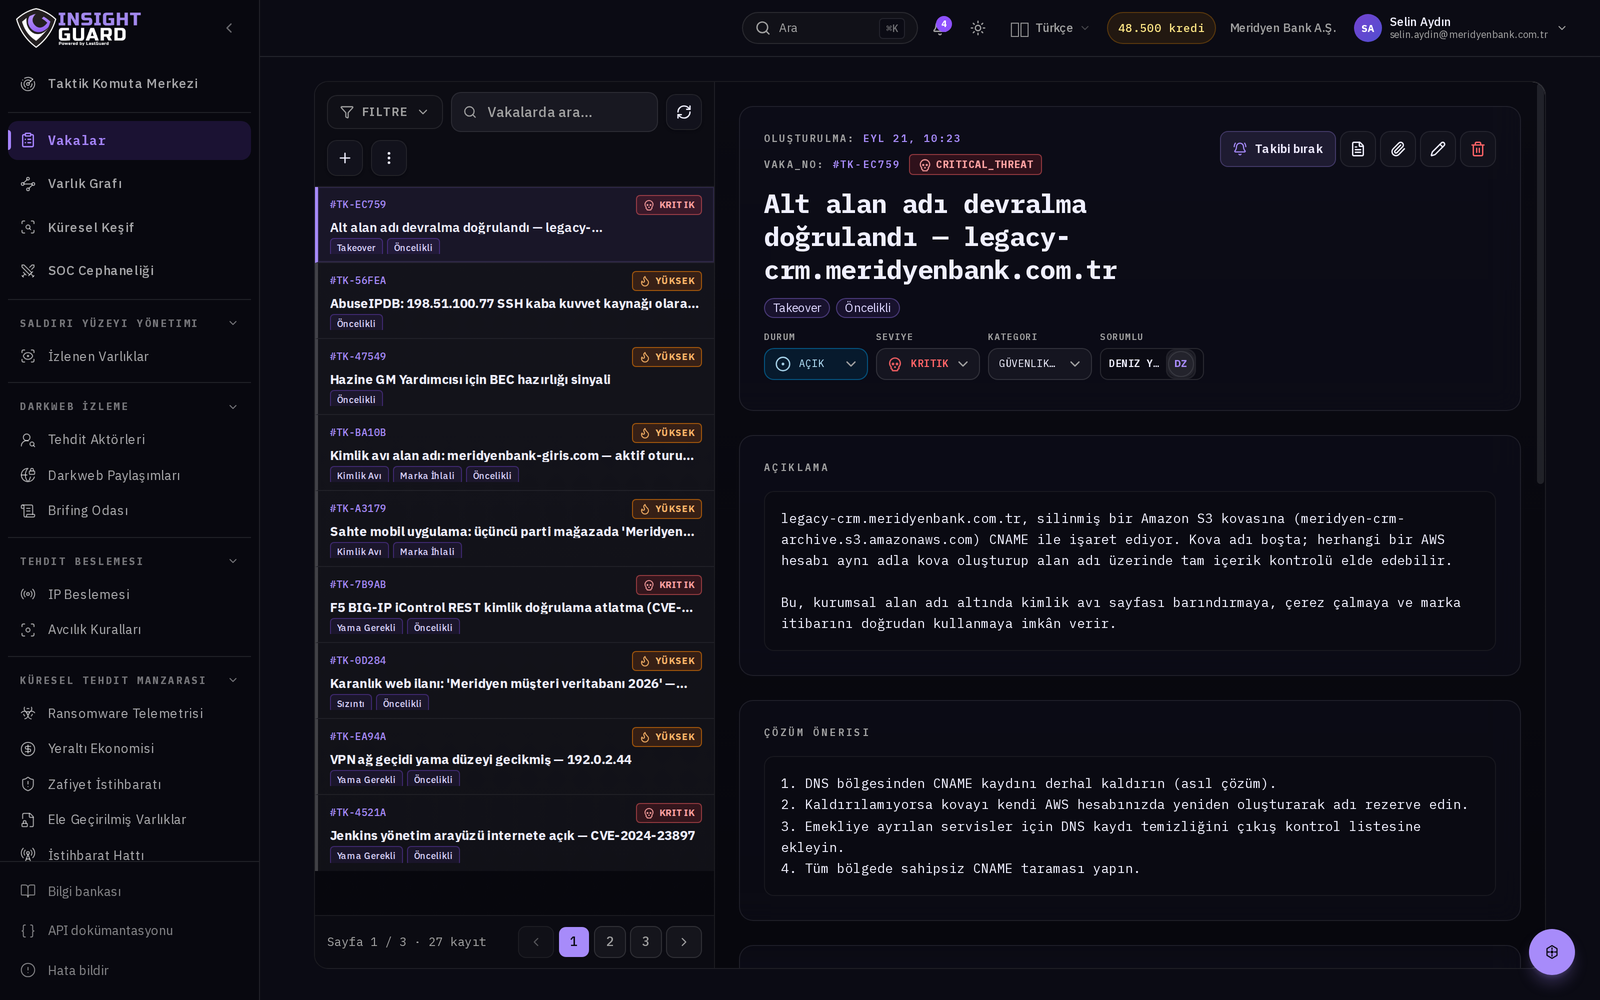
Resolved, false positive and risk accepted are not the same thing. Getting the distinction right determines what your report says …
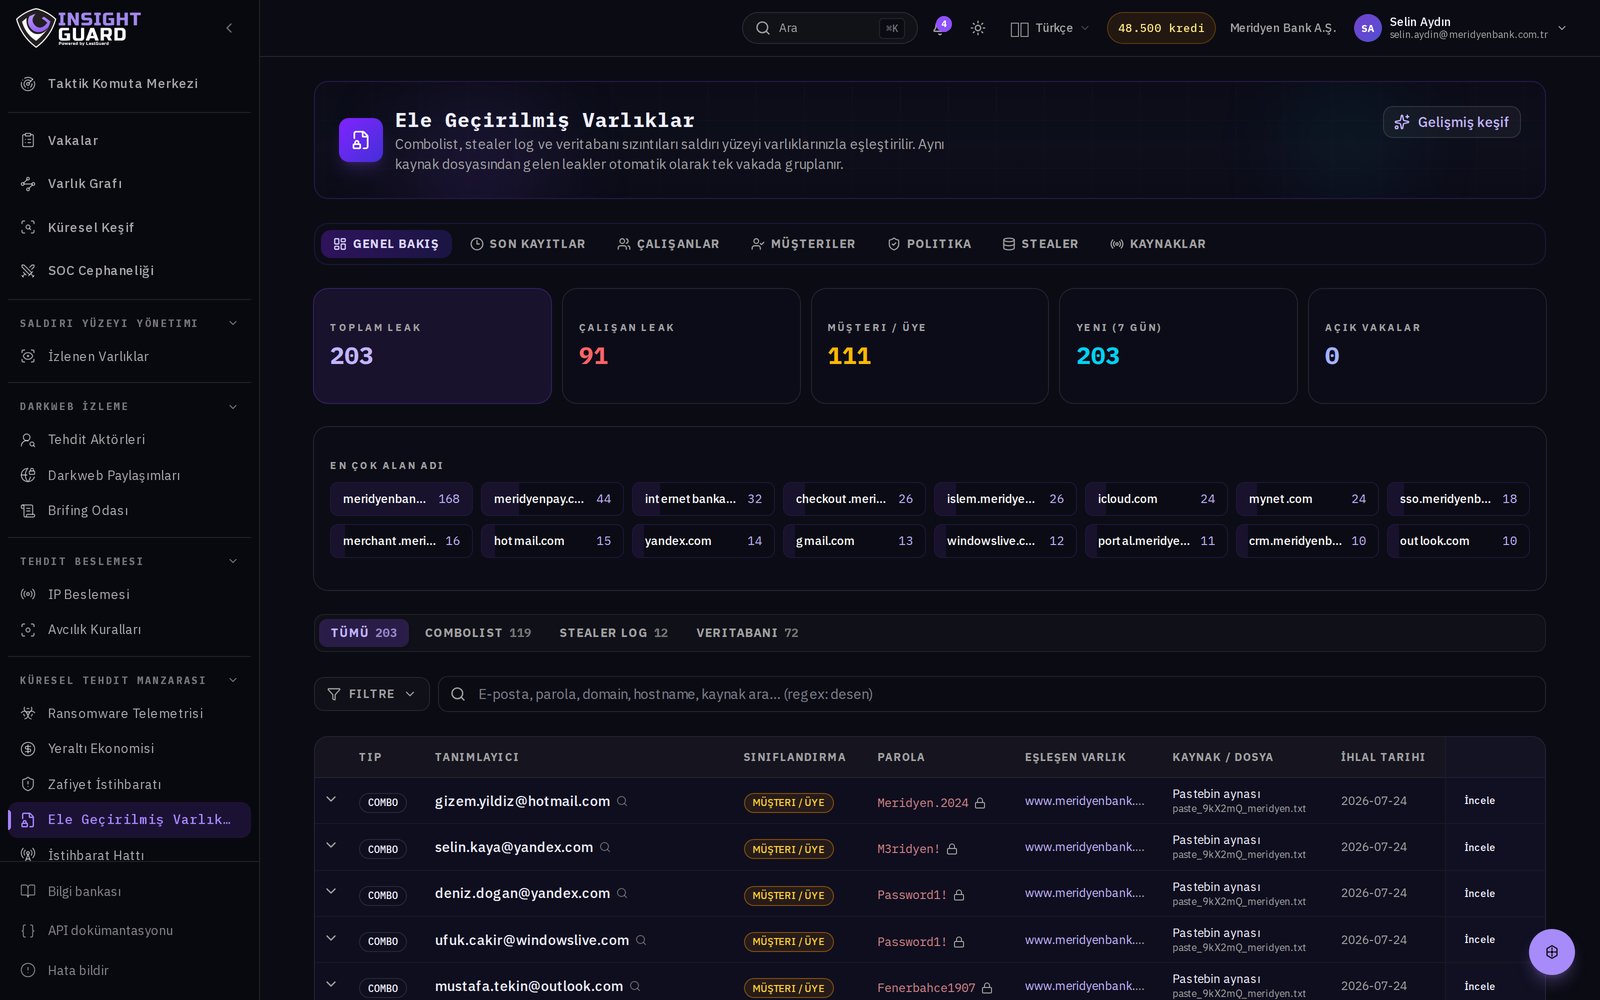
A valid session cookie removes the attacker's need for both the password and MFA. Case closure starts with session revocation.
Most fake domains obtain a certificate before they go live. That is a window to see the campaign before its …
Listing technique IDs is not a coverage analysis. The real question is whether that technique is visible in your environment.
When a DNS record outlives the resource behind it, someone else can claim the name. Nobody notices, because nothing breaks.
Reducing alert volume is an outcome, not a goal. The goal is that every alert can be tied to a …
A finding without an owner never closes; without a closure rationale it reopens three months later. We made both mandatory …
CT logs are the cheapest way to find assets outside your inventory. They are noisy, but the noise is manageable.
Closure is the most rushed step of a case. Five questions stop the same finding coming back three months later.