CT logs are the cheapest way to find assets outside your inventory. They are noisy, but the noise is manageable.
Certificate transparency logs publicly record every certificate issued for a domain. That makes them the lowest-cost way to find subdomains created without your organisation's knowledge.
What surfaces
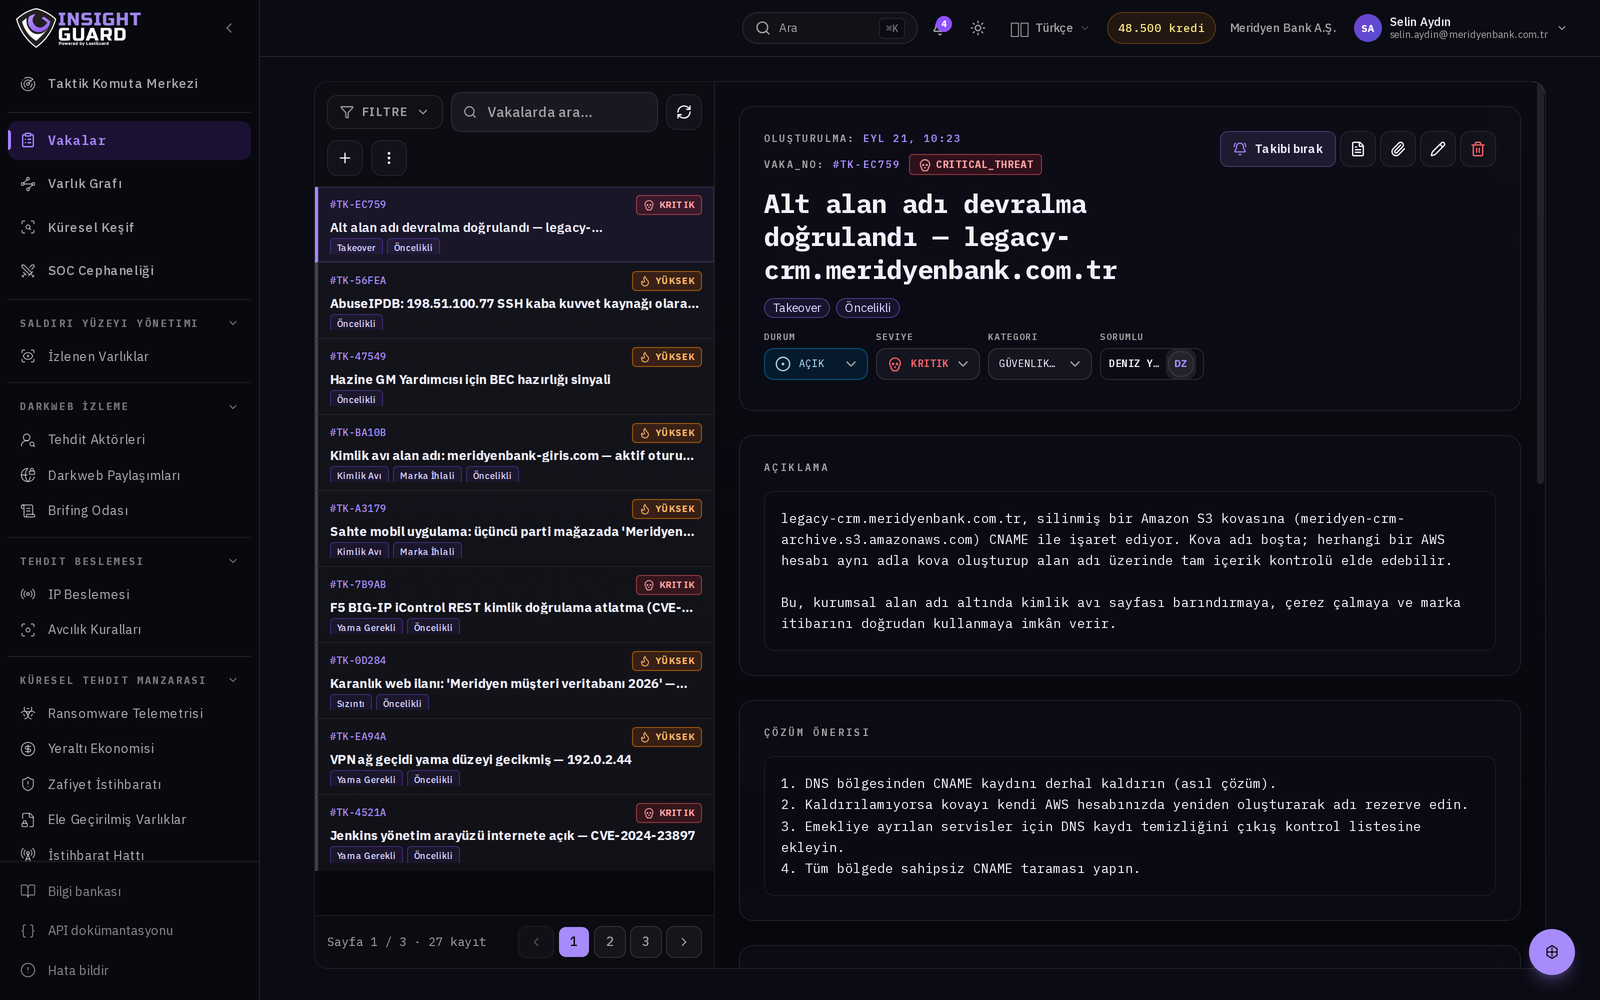
- Test environments a team spun up in its own cloud account.
- Temporary names created for a campaign and never retired.
- Names inherited from an acquisition and never recorded.
- Third-party registrations imitating your brand.
Reducing the noise
The raw feed is very wide. Three filters make it workable: does the record resolve to an A/AAAA, which provider issued the certificate, and does the name match your known naming pattern. Names that do not match but do resolve take priority.
The limit
CT only sees names that obtained a certificate. A service not serving HTTPS, or a panel reachable only by IP, will not appear; passive DNS and port scanning have to fill the gap.